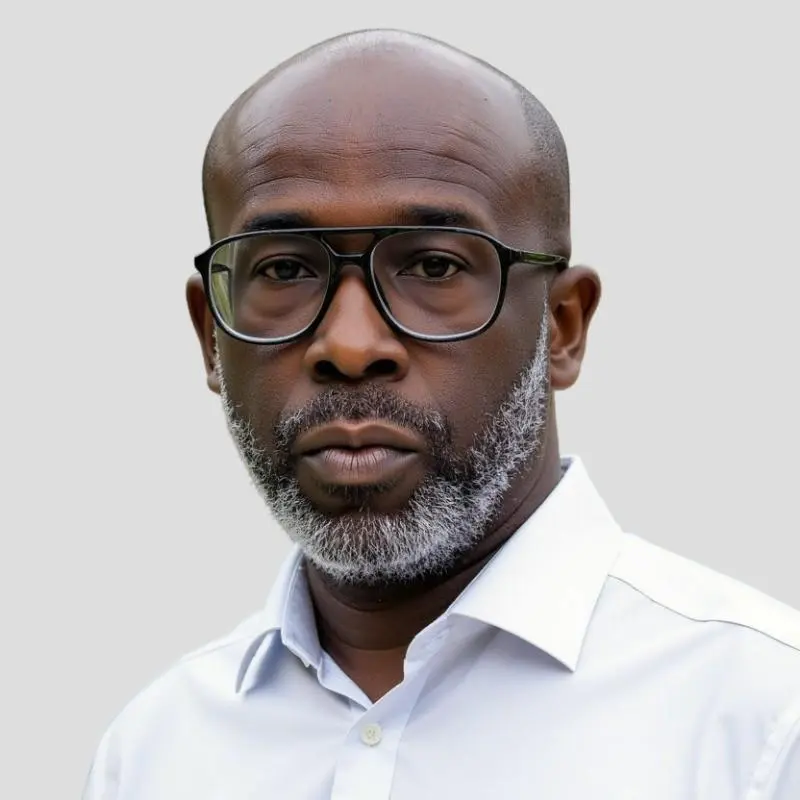
Caption: Niel Harper
In Brief
- Outdated legislation: Cybersecurity expert Niel Harper says T&T’s Computer Misuse Act is roughly 25 years out of date, while the Cybercrime Bill has been stalled in Parliament since 2014.
- Data privacy gaps: Although the Data Protection Act exists, it is only partially enacted, and the country still lacks an Information Commissioner to oversee compliance and educate the banking and energy sectors.
- Missing strategy: While T&T has a strong Computer Security Incident Response Team (CSIRT), it lacks a dedicated national cybersecurity agency to drive overall strategy.
- The solution: Harper urged T&T to join international frameworks like the Budapest Convention to help fast-track modern cybercrime laws.
By Sue-Ann Wayow
PORT OF SPAIN — Trinidad and Tobago is relying on legislation that is more than two decades out of date to police malicious online activity, leaving “critical gaps” in the nation’s digital defences, cybersecurity expert Niel Harper warned on Wednesday.
Speaking at AMCHAM T&T’s 30th Annual HSSE Conference and Exhibition at the Hyatt Regency, Harper delivered a stark assessment of the country’s legislative and regulatory framework, pointing to a 26-year-old Computer Misuse Act, a partially proclaimed Data Protection Act, and a Cybercrime Bill that has languished in Parliament for over a decade.
Harper said, “Your Computer Misuse Act, which addresses the misuse of online systems—to attack a business, to attack an individual, to engage in malicious activities online—is around 25 or 26 years outdated.”
He also noted that while the cybercrime landscape has shifted substantially in recent years, T&T’s Cybercrime Bill has been sitting in Parliament since 2014 without being effectively debated or enacted.
Data privacy and the missing commissioner
Beyond cybercrime, Harper highlighted major deficiencies in how citizens’ personal data is regulated. He pointed out that while the Data Protection Act has been on the books for several years, it remains only partially enacted.
As a result, critical mandates—such as the registration of data processors and the requirement for businesses to appoint internal officers responsible for protecting individual privacy—are still not in force.
“You still haven’t hired and put someone in charge of your privacy legislation,” Harper said. “You don’t have an Information Commissioner who is overseeing how data controllers and data processors are being managed in the country.”
He explained that an Information Commissioner is vital not only for enforcing the law, but also for building awareness and engaging key industries—such as the banking and energy sectors—to help them understand their privacy responsibilities and how to comply.
The need for a national agency
Harper acknowledged that Trinidad and Tobago has made positive strides in some areas.
He praised the local Computer Security Incident Response Team (CSIRT) as a leading institution in the region for preparing the country to handle cyber incidents, and commended the telecommunications regulator for developing a framework to make service providers more resilient to operational disruptions.
However, he said that significant vulnerabilities remain without a central body to coordinate the country’s defence.
Harper said, “There is no national cybersecurity agency responsible for your overall national cybersecurity and strategy.”
He said that such an agency was necessary to bring stakeholders together and make T&T more resilient against international threat actors.
Harper suggested that Trinidad and Tobago look outward and become more involved in multilateral discussions, pointing to global frameworks such as the United Nations Treaty on Cybercrime and the Budapest Convention.
He said, “If Trinidad and Tobago is more involved in international discussions and decides to accede to the Budapest Convention, that is a really good driver—a mandate to bring your Cybercrime Bill into force and start to address cybercrime from a modern perspective.”
See related stories below:
Beyond the Factory Floor: Justice Seepersad Calls for Psychological Safety at Work
‘People are Tired’: AMCHAM President Calls for Rethink on Safety, Burnout, Productivity
See Winners: 16th Annual National Excellence in HSE Awards
Safety on Trial: Om Lalla on Why Paper Policies Fail in the Courtroom
When Systems Fail: Niel Harper Warns Cyber Threats are now Physical Safety Risks